Showing posts with label google. Show all posts

Friday, November 6, 2015

There are tons of websites to find a job, that's the thruth


There are tons of websites to find a job, that's the thruth

So? There has been a long time since my last post, I've been starting so many projects including some business and stuff and today I'm back to write about this topic which is not even close about the last posts.

So if you are looking for some networking or computing cheat, that's not your post :)

I'm here to think and write about job hunting websites and all about those things.

There was an age...


There was an age where sites like linkedin and infojobs were cool sites to find a job, but, to be honest the have lost that charming brand new magic and they are just a huge curriculum store.

And now what? what's the trend?

That's the point, there are no reference in this matter, it becomes a problem when you are trying to upload your CV to the Internet because you need to keep up-to-date from three to ten profiles in different websites which are roughly the same thing.

There are no fashion sites, the trend now is that there is no trend; and that's a real problem.


I've no tips about which site is the best, so that's my idea, create your own.
Maybe it looks a bit crazy, but it's just an idea.

My own site? What kind shit is that?

Ha ha! You may be right, it could be crappy if you do by the wrong way and the problem is... that there is no best-way but I think that this may be a good chance to take the attention about a head hunter / human resources crew if you make the difference by sending your CV just all-in-one by sending a URL.


Some examples?

I've no examples but I have some ideas to tell to you:

- Create a easy-quick-free site using services like blogger. This is easy to do and free, the only problem may be the low customization level.
            www.blogger.com

- Contact with cheap webhosting services like 1and1 "my web" or something like this, they are intended for small business but you can try it. They have medium customization level.
           www.1and1.com

- You can try too by contacting the MiniWeb guys, they are a brand new website design&hosting company, they just started a few months ago but they are doing quite well. You can contact them both in English or Spanish, you'll find a very cheap service packs. Can contact by facebook, twitter or send a message from the web form contact.
          www.miniwebspain.tk


We are legion

Tuesday, January 20, 2015

My preferred linux distros. Wireless auditory

Hello there,

Long time ago from my last post, there were too many changes in my life but finally I'm back :)

Today we are here to discuss about current linux live distros for wireless auditory.

There were many changes during this while, lots of linux flavours with many wireless audit tools already installed and ready to run live, persistent or installed on your hard disks but today I will write for my favourites.

  • Xiaopan OS (the tiny one)
  • WifiWay / WifiSlax (actually, the same)
  • Kali (huge, a beast)

The tiny one, Xiaopan OS

Xiaopan Logo

You can download the ISO file from http://sourceforge.net/projects/xiaopanos/   just ~70 Mb and all the info about it at http://xiaopan.co/


From it's own website we get this comments:

Xiaopan OS is an easy to use security and penetration testing with a collection of wireless security and forensics tools. It includes a number of advanced tools for network administrators, security professionals and home users to test the strength of their wireless networks and eliminate any vulnerabilities.
Xiaopan (0.4.7.2 is the latest)

I've tested this distro three times:
The first one: my desktop computer, It worked great live from my USB device, I tested many tools and opcions, all working fine. It's tiny but powerful.
The second one with my laptop, it was unable to detect my wireless network interface, testing tons of "solutions" from the Xiaopan forums, end of story :(
The last one: With my girlfriend's notebook, same as the previous one, wireless interface not detected.

So, my conclusion is that Xiaopan is a very light linux distribution full of options and utilities but it needs a few more controllers and drivers to be widely compatible to many computers and devices. It will be great in the near future, I hope.


WifiWay / WifiSlax

These are awesome linux distributions that I love, it's light enough to be stored in a cheap USB device but has drivers, utilities....  enough to be a great penetration testing linux distribution.

WifiSlax Logo


We can call them the twin distributions, you can test both of them, they are likely the same but from time to time one of them releases a new version, so, I switch between them properly.

You can download it from http://www.wifislax.com/category/download/nuevas-versiones/
Its website has many tutorials and news it Spanish but you'll be able to translate it with no problem, all of them are plenty of photos and videos where you can find all then info you may need.

Both distributions will work great both live or persistent (obviously installed too). I used to test many linux distributions but I'm always  back to WifiSlax when I need to do something important, with no problems, no issues, just working quick and fine.


Kali

It's, (said by their own website) the rebirth of BackTrack, if you know, that's the only presentation that it needs.
BackTrack was the best well-known penetration testing linux distribution in the world, everybody loved it; and now, everybody should love Kali too.

I say that because there are a few changes in the way it works (most of them have improved it) but there are many nostalgic people who misses backtrack.


Kali Logo
You can download Kali here https://www.kali.org/downloads/


 There are many Kali versions, for 32 bit, 64 bit, for ARMEL chips, for ARMHF chips... eventualy you have the chance to download the core and build a custom version for your own.


In summary, it's a huge linux looking at the tools, functions, utilities... it has all you will need for seven lifes! But, it's (from my point) too big for live USB. I mean, it works live from USB but it's not as responsive and quick like WifiSlax


I always love to summarize with images to make things easier to think, that's my view of these distros:

WifiSlax

Xiaopan
Kali


Xiaopan, you'll feel like Bart Simpson
WifiSlax, quick and effective.
Kali, huge and powerful.

In the next post I will write about how to make your own linux USB bootable.

We are legion


Saturday, May 12, 2012

Windows 8 will not allow SW non-MS SW

Hello all,

A few days ago we read at the Mozilla forums:
"an unwelcome return to the digital dark ages where users and developers didn’t have browser choices."Said by Harvey Anderson, general counsel in Mozilla co.

Do you have to imagine a future only with MS apps? You won't be able to use Firefox, Chrome, WinZip, WinRar, WinAmp...


Some art in the street:


Some people could think "who will buy a OS which will not allow me to decide which internet browser I want?"

Even: Who the hell is going to buy that?

My own opinion: "Nobody!!!!!!!"


Which could be the explanation for this behavior?

Easy to answer too :) It is the kind of action undertaken by a company that has lost its way.

Really, does anybody think that this action will help them? I really think that this action will definitely push people to try Linux/Unix at home, don't you know?

If you are one of those users, I will recomend you Ubuntu or even BackTrack :)

Thus, this image will take sense, right? :)


I know that is a very short post, but.... I HAVE TO inform of this, I think is absolutely needed.


Next post: "My preferred linux distros. Wireless auditory" (English)
Siguiente post: "Mis distribuciones favoritas de Linux. Auditoria WiFi" (Español)


We are legion

Friday, March 23, 2012

Reaver (WPS attack) and WPAMagicKey tools (Spanish)

wep wpa WPA 
(Esta es la versión en Español de un post reciente | This is the Spanish version of a previous post)


Hace unos meses se escucho: "WPA ha caido, lo hemos crackeado!"

Mentira cochina, es absolutamente falso, nadie ha crackeado este algoritmo de cifrado. Hoy, esta sera nuestra idea principal.
Por lo menos, nadie ha publicado nada sobre como crackear WPA. Hace ya mucho tiempo que se abrió la forma de crackear WEP pero todavía no es la hora de WPA (WPA2 va incluido cuando hablamos de WPA)
Hay algunas formas de acceder a redes wifi con WPA habilitado pero ninguno de ellos podria llegar a ser llamado "cracking" como tal:

- Capturar el handshake de WPA - TKIP (aircrack + diccionario): esto no es cracking porque necesitarías un diccionario a posteriori para poder obtener la contraseña. Sin diccionario previo, no serás capaz de obtener nada.
- Usar WPA Magic Key  (sin aircrack): Esta herramienta puede generar una lista de contarseñas por defecto para routers WiFi de los tipos WLAN_XXXX o JAZZTEL_XXXX y que además se cumpla de que nadie haya cambiando nunca su clave (son las que vienen por defecto). Esta herramienta no calcula la clave, simplemente la saca de una lista de candidatas.
- John The Ripper (para usar con aircrack): Puedes generar tus propios diccionarios if sabes el patron que va a seguir la contraseña y además no es una contraseña demasiado larga (menos de 4 - 5 caracteres), si es muy larga tu diccionario tendría un tamaño imposible de manejar, totalmente inmenso. (Ver la tabla y grafico a continuación)


De los calculos en la tabla anterior, puede ser una muy mala idea intentar crackear una clave por fuerza bruta en una red inalambrica WPA.

En el grafico anterior podemos comprobar que la mayor parte de las contraseñas suelen ser del tipo más complicado de sacar (de caracteres mezclados)

Entonces, ¿estamos bastante seguro de que nadie ha crackeado una WPA, no?

Desde el punto del vista del hacker, la diferencia más importante entre WEP y WPA is lo que se trasmite dentro del paquete IP. WPA nunca va a introducir en la transmisión ninguna información relativa a la clave maestra de la red, lo anterior no es correcto en el caso de las redes con cifrado WEP.

En el grafico siguiente podemos ver un pequeñisimo esbozo de como se contruyen los paquetes en base a claves que a su vez derivan de la clave original. De ahí que no haya datos de la clave original en la transmisión.

Ahora deberíamos aprender algo más de WPS (Wikipedia). La forma mas simple y sencilla para tener en mente lo que es WPS: "WPS es un botón". Si así como suena, es un botón que te deja conectarte a la Wifi, o no.
Finalmente, si nadie ha sido capaz de crackear una WPA, ¿Que demonios es reaver? ¿Que puede hacer por mi? ¿Voy a ser capaz de usar reaver?

- Reaver: Es una herramienta script que utiliza la vulnerabilidad WPS para engañar al router y hacerle crear que estamos haciendo una configuración remota del router, en la que le solicitamos algunos datos, como por ejemplo... que se yo... la contraseña?  :)
- Por lo que yo se, reaver solo va a poder ayudarte mientras la red esté utilizando TKIP (no soportado para AES, aun!!!)
- Previamente, antes de ejecutar "reaver" deberías ejecutar la herramienta "walsh", que es un script que te va a avisar de que redes inalambricas en tu alcance serían susceptibles de poder atarcarse.

Hay montones de video tutoriales sobre reaver... (mi favorito es el primero)
Video#1 (en este te van a explicar como instalar, es muy bueno, en Inglés)
Video#2

También podrias necesitar estas pistas

In la mayor parte de los casos podrás obtener reaver en distribuciones linux como BackTrack o WifiWay.
En alguno de los próximos post hablaremos de la nueva versión de WifiWay (v. 3)

Ya sabemos que no se debe utilizar para hackear, tienes que utilizar esto exclusivamente para seguridad, vale?

Somos legión

================================================================
Siguiente Post: "PayPal is vulnerable, XSS"

Google Hacking, cuidado con tu sitio web!!! (Spanish)

(Esta es una versión traducida de un post anterior en Ingles - This is the Spanish version from a previous one in English)

¡Hola!
Hace mucho tiempo del último post, he estado muy ocupado los últimos meses.
Estamos de vuelta otra vez a hablar de un estilo antiguo clásico de hacking: "Google Hacking".

Esta forma es muy simple ya que no requiere ninguna herramienta avanzada o software, se puede hacer simplemente con una conexión de módem de 56k a Internet (Aunque realmente espero que tu conexión es un poco más rápida!!)

Todos nosotros sabemos de los algoritmos de búsqueda avanzados y recolección de datos de gran potencia de Google, creo que Google es el buscador más avanzado tecnológicamente en el mundo en este momento (en los últimos 5 - 10 años).

Google es mucho más que un cuadro de texto y un botón de "Buscar", e incluso mucho más que un "voy a tener suerte" :)

Debemos saber que Google tiene capacidad de recoger datos de archivos que no sean clásicos de las páginas web html, cada día Google está detectando una gran cantidad de archivos pdf, doc, ... .

Google tiene muchas opciones y filtros de búsqueda avanzada, como la búsqueda por tipo de archivo, por parte de texto en una dirección web (url), por la extensión de archivo ...

Este mecanismo es simple como:

- Búsqueda de doc. Watson informa de un servidor
- Buscando información importante de los datos personales
- Búsqueda de archivos con cuentas de usuario
- Búsqueda de archivos con usuarios y contraseñas!!

Sí, por supuesto, toda esta información está ahí, tenemos libre acceso, a muchos archivos sólo a través de Google.

Puede acceder a la ayuda de Google con el fin de aprender "comandos" para llevar a cabo algunas búsquedas avanzadas.

Recientemente, este tipo de piratería informática fácil y simple fue utilizado contra muchos organismos de seguridad importantes de los EE.UU. y Europa Occidental.

Este método puede ser considerado "Ingeniería Social"

----------------------------------------------------------------------------------------------

Somos legión.
Siguiente post:
"Reaver (WPS attack) and WPAMagicKey tools"

PayPal is vulnerable, XSS

(There is another post in Spanish | Puedes acceder a la versión de post en Español aqui)
Today, here we are with the next post about a kind of hacking.


A few months ago (about December'11) two Indian hackers were able to launch an attack using the URL from the PayPal site.
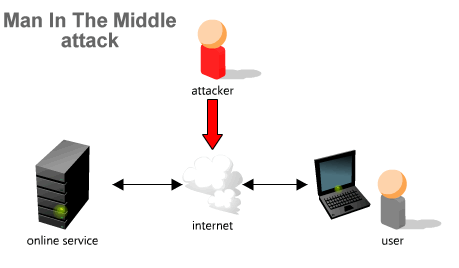
That not means anything about the server breaking-into, this is not correct. But that could mean a "Man in the middle" attack (MITMA).


Why wanna do with a MITM attack?
Easy to know, to review and steal your sensitive information like user accounts and passwords, bank accounts...


What's a "man in the middle attack"??


We will supose: I want to launch a MITM between Google and a friend's pc. I'll need a software to "cheat" my friend's pc (i.e. Metasploit). When he writes google.com he won't access to google,he'll access to my pc camouflaged as Google web site and I will be connected to the real Google server.

In the image (right), "Web Server" could be Google in our example and the victim PC is our friend's PC.


In the image (left), the victim is "authorized user". The attacker say to the access point (AP) that he is the authorized user and the attacker say to user that he is the AP.


By the way, the attacker will be in the middle of the data traffic.

Thus, the authorized one will think that he is directly connected to the corporate LAN but the attacker will be seeing all his data transmission.


Then, what's XSS - (Cross Site Scripting)???


XSS is a kind of vulnerability directly related with websites and/or web applications that allows an attacker to send data bypassing server validations. This vulnerability could cause a few kinds of attacks: persistent, non-persistent...

In summary (if your an expert hacker you will feel stomach ache with this summary and definitions, it's just for let a simple definition for non-experts):

- If the hacker "cheat" the remote user and use its data to access the server data, it's non-persistent XSS attack
- If the hacker "cheat" the server admin user and use its data to access the client data, it persistent XSS attack

For the second type, this is a graphical explanation:


If you wanna get more advanced definitions about XSS, click here.
------------------------

We are legion.
Next post: "HOIC: new improved version of LOIC"

Wednesday, March 14, 2012

Google Hacking, be careful with your web site!

(Now you can access to the Spanish version of this post | Puede acceder a la versión en Español de este post)

Hi there!
Long time ago from last post, I was very busy last months.
We're back again to talk about a old-classic way of hacking: "Google hacking".
This hacking is very simple a it doesn't require any advanced tool or software, it can be done just by using a 56k modem connection to the internet  (I really hope your connection is a bit faster than this  :D   )
All of us know about the advanced search algorithms and powerful data pickup of Google, I think Google is the most technologically advanced search engine in the world right now (in the last 5 - 10 years).
Google is much than a text box and a "Search" button; even much higher than a "I'm feeling lucky" button  :)
We should know Google has able to pickup data from other files than classic html web pages, every day Google is detecting a huge amount of pdf, doc,... files. Google has many filter and advanced search options, like search by filetype, by some text in a web address (url), by file extension...
This mechanism is simple as:
- Searching Doc. Watson logs from a machine
- Searching important information about personal data
- Searching files with users accounts
- Searching files with user and passwords!!!!
Yeah, absolutely, all of this info is there, we have free access at many files just using Google.
You can access to google help in order to learn about Google "commands" to perform some advanced searches.
Recently, this easy simple hacking type was used against many important security organisms from the U.S. and West-Europe.

This method can be considered "Social Engineering"

We are legion.
Next post: "Reaver and WPS attack"

Popular Posts